Audit Log
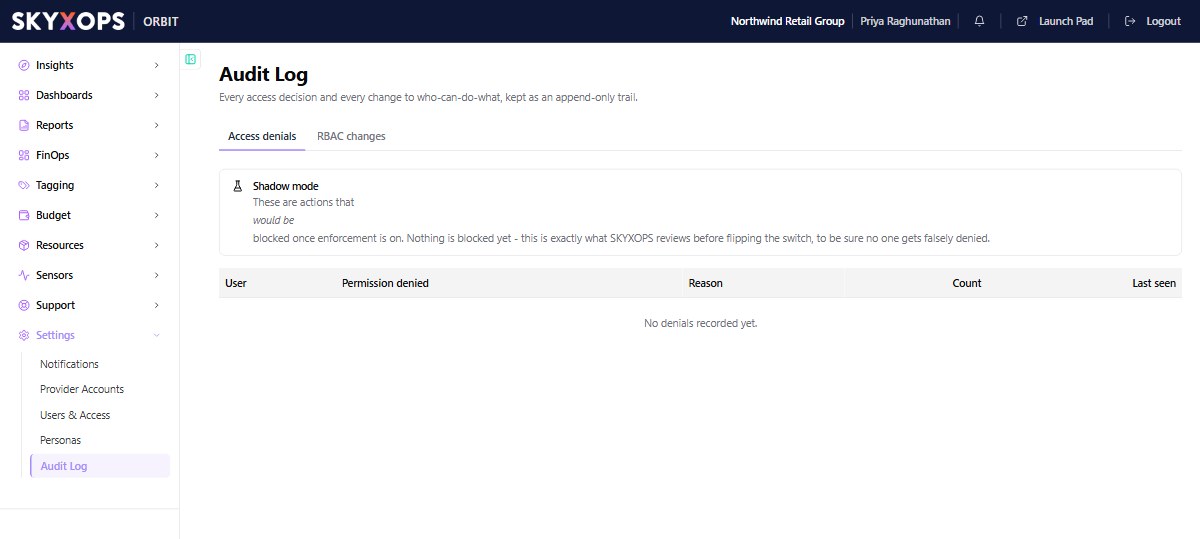
The Audit Log (Settings > Audit Log) is an append-only record of every access decision and permission change in your Orbit workspace. It answers who changed what, and when?
What's recorded
| Entry type | What it covers |
|---|---|
| User changes | Invites, persona assignments, and deactivations from Users & Access. |
| Permission changes | Edits to personas and their permission matrix. |
| Access decisions | Grants and denials as people use the app. |
Each entry is immutable. The log can be read but not altered, which makes it suitable for security review and compliance evidence.
Reading denials while access control is in shadow mode
Enforcement isn't switched on yet (see Users & Access), so a logged denial records what would have been blocked. The person was not actually stopped. Treat these entries as a preview of your permission model. Do not treat them as evidence that access was prevented.
Using it
Open Settings > Audit Log to browse the trail. Use it to:
- confirm a permission or user change happened, and by whom;
- investigate an unexpected access denial;
- produce an access-history record for an auditor.
FAQ
Can entries be edited or deleted?
No. The log is append-only by design.
Who can view it?
Administrators whose persona grants access to the access/audit area.